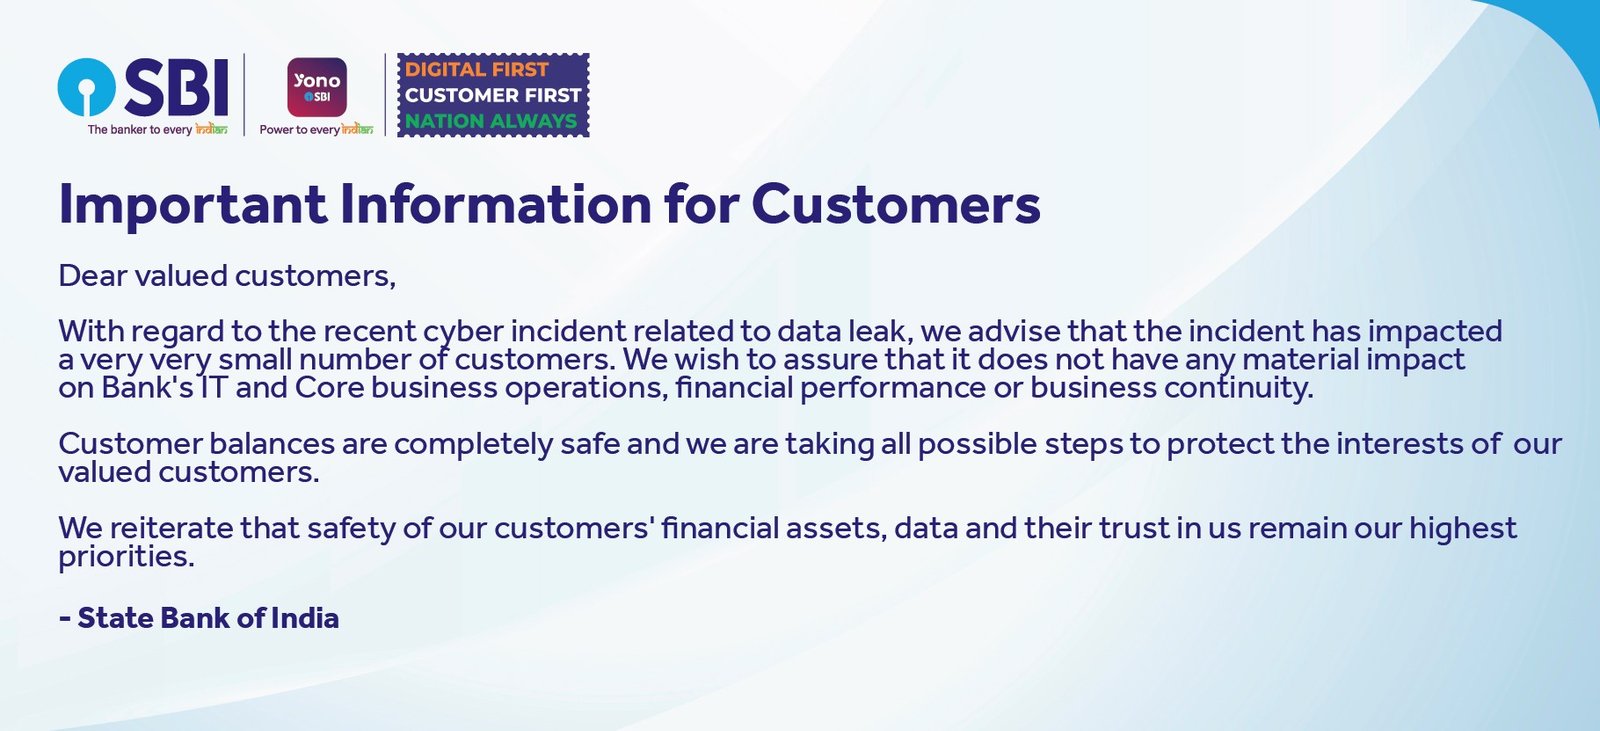
MUMBAI, October 22 (Aalimi Nation) – State Bank of India has confirmed that the personal details of 3,897 of its customers were found on the dark web, in a disclosure to the stock exchanges on Wednesday. The country's largest lender said the incident has no material impact on its core business, and that an independent investigation is under way.
In its filing, made under the stock exchange disclosure rules for listed companies, the bank said it received communications on October 16 from the Defence Cyber Agency, its threat intelligence service provider, and the Indian Computer Emergency Response Team, CERT-In. Both flagged a suspected exposure of customer data on the dark web.
The bank's preliminary analysis covered roughly 3.75 lakh records, of which 3,897 were identified as customer records containing personal information. The fields involved include names, registered mobile numbers, dates of birth, gender, email addresses and residential addresses, along with branch and customer information file identifiers, lead IDs and metadata linked to loan and lead records.
The bank said it activated its cyber incident response and containment protocols and engaged an independent cybersecurity agency empanelled by CERT-In to examine the nature and extent of the alleged compromise. It said a detailed assessment was under way, and that it would take all appropriate measures in line with regulatory requirements.
The bank said the authenticity and completeness of the data, as well as its likely source and extent, still have to be established. The filing does not say how the information left the bank's systems, whether it came from the bank itself, a subsidiary, a vendor or a sales agent, or whether any customers beyond the 3,897 are affected. It also does not say whether those customers have been told individually.
Under directions issued by CERT-In in April 2022, organisations must report cyber incidents within six hours of noticing them or being alerted. Reserve Bank directions issued on July 31, 2026 also require banks to report incidents within six hours of detection.
The Internet Freedom Foundation has argued that the Digital Personal Data Protection Act requires notification of the Data Protection Board and of each affected individual. It has asked SBI to inform every affected customer directly, explain what was exposed and advise on protective steps. It also wants the Reserve Bank to direct regulated entities to notify customers, and the electronics and information technology ministry to bring the relevant provisions of the data protection law into force immediately. It said the detailed notification rule takes effect only on May 13, 2027.
Security specialists generally advise customers to treat unexpected calls, messages or emails that mention loans or personal details with caution, since leaked contact data is often used for phishing. Customers are advised never to share one-time passwords or PINs, to verify any request through the bank's official channels, and to report suspected fraud on the National Cybercrime Reporting Portal or by dialling 1930.
The findings of the independent assessment and whether SBI begins notifying affected customers are the developments to follow.